Crypto Scammer Returns $9.27 Million Out of $24M Crypto Theft

0
[ad_1]

Crypto scammer sensationally returns $9.27 million to a victim after $24 million theft. Unprecedented move in crypto crime. Scam Sniffer reveals shocking details.

A crypto scammer has returned $9.27 million in stablecoins to a victim. This restitution, equating to 38.26% of the total stolen amount, was reported by Scam Sniffer, an anti-scam platform focused on the cryptocurrency industry.

Scam Sniffer disclosed the details of this unusual event on its official X account, revealing that the original theft occurred in September 2023. During this incident, the victim lost $24.23 million in various crypto assets, including rETH and stETH coins.

The scam was executed through a sophisticated phishing attack which successfully deceived the victim and resulted in the loss of such a significant sum. Scam Sniffer pointed out that the victim signed off on “increaseAllowance” transfers, a common tactic used by scammers to gain access to a victim’s crypto holdings.

Further investigation by Scam Sniffer linked the scammer’s address to several phishing websites within the crypto space. Additionally, some of the stolen funds were moved to @FixedFloat, a platform known for its rapid crypto exchange services.

This partial restitution of funds represents an unusual and rare occurrence in the world of crypto scams, bringing a glimmer of hope to victims of such fraudulent schemes.

Not the first time

This is not the first time that a scammer has returned some of the stolen crypto to their victims. There have been numerous such cases in the past, for instance, the following:

March 2018Hacker returned $17 million worth of stolen Ethereum

April 2020Hacker returned $25 million after their IP address was exposed

October 2020Hacker stole $24M, returns $2.5M to Harvest Finance DeFi

January 2020Multichain hacker returned $1m, keeps $150k as a bug bounty

March 2023Hacker Returned $200 Million Stolen from London’s Euler Finance

If your business involves cryptocurrency-related legal activities, you require the highest level of security to protect not only your assets but also customer funds and data. For your convenience, here is a list of the 6 best crypto bug bounty programs.


[ad_2]
Source link
Hackers Exploited Windows MSHTML Vulnerability For Over A Year

0
[ad_1]

Researchers revealed that the recently patched Windows MSHTML vulnerability remained under attack for over a year before Microsoft could fix it. While the vulnerability has now received a patch, it remains crucial for all vulnerable systems to apply the fix and scan their systems for potential infiltration.

Windows MSHTML Vulnerability Exploit Works Against Windows 10, 11 Alike

According to Check Point Research (CPR), criminal hackers had exploited the recently fixed Windows MSHTML vulnerability for eighteen months.

As explained, the exploit worked because of the vulnerable “mhtml” trick that allowed the adversary to call Internet Explorer instead of Microsoft Edge.

While Microsoft has replaced the Internet Explorer browser with Microsoft Edge, ending support in 2022, it remains somewhat accessible on Windows 10 systems, where it was available at the time of OS launch. In fact, CPR observed the same behavior with the latest Windows 11 too, which makes even the most recent Windows systems vulnerable to the MSHTML attack.

Regarding the exploit, the researchers stated that the attackers used a previously unknown trick to lure users into opening maliciously crafted files. The trick allowed the attackers to create files with .url extensions, which would call Internet Explorer due to the use of mhtml: URI handler.

However, to evade detection, the attackers hid the “.url” extension, making the files appear as PDF files. Clicking the file would open the Internet Explorer browser, downloading an archive with the data-stealing malware from the attacker-controlled web page. While the process would generate several prompts that may alarm a savvy user, an average user may not pay attention to the prompts, eventually falling prey to the attack.

The researchers have explained the entire attack strategy in their post.

Microsoft Fixed The Vulnerability with July 2024 Patch Tuesday

Upon discovering the vulnerability, Check Point Research reported the matter to Microsoft in May 2024. In response, the tech giant patched the vulnerability with the July 2024 Patch Tuesday updates, disclosing the flaw as a zero-day.

Though the patch has arrived, the researchers still advise the users to remain cautious when opening .url files from untrusted sources.

Let us know your thoughts in the comments.


[ad_2]
Source link

The Impressive Bose SoundLink Flex Bluetooth speaker is now just $99

0
[ad_1]

Amazon has the new Bose SoundLink Flex Bluetooth speaker on sale today, where you can save $50 off of this speaker. Bringing the price down to just $99. That’s a pretty good price for a Bluetooth speaker of this caliber actually. It’s actually a larger discount than that price shows you, this is because Bose rarely ever discounts its products. Typically only around Black Friday/Cyber Monday and Prime Day, and that’s about it. So not only is this price drop rare, but it is also the lowest the Bose Soundlink Flex has ever been.

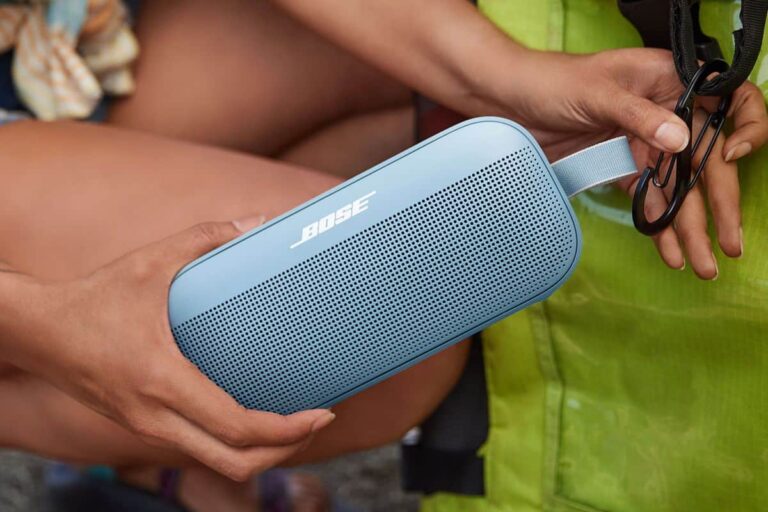
The Bose SoundLink Flex comes in three colors: Black, White, Smoke, and Stone Blue. The Stone Blue is a really nice color, actually. It’s a waterproof speaker (certified at IP67), so you can feel free to take it to the beach, or the lake. And even use it in the shower. Making it great for outdoor adventures.

Bose says that the SoundLink Flex is packed with exclusive technologies and has a custom-engineered transducer for deep, clear, and immersive audio at home or on the go. Thanks to the proprietary PositionIQTechnology inside, this speaker can automatically detect the position of your portable Bluetooth speaker for optimal sound quality in any orientation or environment.

The battery life here is also pretty impressive. We’re looking at about 12 hours of continuous playback. That will get you through a day at the beach without any issues. It recharges using a USB-C port. Which is great to see. As a lot of other speakers are looking to cut costs and sticking with micro USB for charging still.

There’s also a nice carabiner on the speaker, so you can use it to attach to your backpack and listen to music while you biking down a trail this summer. It’s a really great product to take on any outdoor adventure this summer. Especially now that everything is opening up again.

You can pick up the Bose SoundLink Flex Bluetooth speaker from Amazon today by clicking the link down below.

Buy at Amazon


[ad_2]
Source link

Cellopoint Secure Email Gateway Flaw-Attackers Execute Arbitrary Code

0
[ad_1]

A critical vulnerability has been discovered in the Cellopoint Secure Email Gateway, identified as CVE-2024-6744.

This flaw assigned a CVSS score of 9.8, poses a severe risk to organizations using this email security solution.

According to the Twcert report, the vulnerability resides in the Secure Email Gateway’s SMTP Listener component, specifically in versions before 4.5.0. The flaw stems from improper user input validation, leading to a buffer overflow condition.

This weakness allows an unauthenticated, remote attacker to execute arbitrary system commands on the affected server, potentially compromising the entire email infrastructure.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files

Technical Details

CVE IDCVSS ScoreVectorAffected Products
CVE-2024-67449.8 (Critical)CVSS:3.1/AV:N/AC:L/PR:N/UI:N/S:U/C:H/I:H/A:HSecure Email Gateway before version 4.5.0

Cellopoint has responded promptly to this critical issue by releasing a patch, Build_20240529, which addresses the vulnerability.

All organizations using the affected versions of Secure Email Gateway must install this patch immediately to mitigate the risk of exploitation.

The discovery of CVE-2024-6744 highlights the ongoing challenges in securing email gateways, which are critical components of enterprise communication infrastructure.

An attacker’s ability to execute arbitrary code remotely without authentication underscores the importance of regular security updates and vigilant monitoring. Cellopoint has been credited with identifying and addressing this vulnerability.

The public disclosure of this flaw on July 15, 2024, aims to ensure that all affected users are aware and can take necessary action to protect their systems.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo


[ad_2]
Source link

Vulnerability In A WordPress Calendar Plugin Actively Exploited

0
[ad_1]

WordPress admins running the Modern Events Calendar plugin on their websites must rush to update their sites with the latest plugin release. That’s because hackers have started exploiting a serious vulnerability in the Calendar plugin to target WordPress sites.

Modern Events Calendar Plugin Vulnerability Risks 150K Sites

The WordPress security service Wordfence recently shared details about a serious security vulnerability in the Modern Events Calendar plugin.

As explained in their post, the Modern Events Calendar plugin had an arbitrary file upload vulnerability. The flaw appeared due to missing file type validation in the plugin’s set_featured_image function. An adversary could exploit this flaw to upload malicious image files or .php files on the target server to trigger remote code execution.

While exploiting the flaw required the attacker to have authenticated access, unauthenticated attacks could also become possible on sites allowing unauthenticated event submissions. In the worst exploitation attempts, the vulnerability could even allow a complete website takeover via webshells or other techniques.

The vulnerability received the CVE ID CVE-2024-5441, achieving a high severity rating and a CVSS score of 8.8. Wordfence has shared the detailed technical analysis of the flaw in its post.

Patch Your Sites ASAP as Hackers Actively Exploit The Flaw

The vulnerability first caught the attention of security researcher Friderika Baranyai (alias Foxyyy), who then reported it via Wordfence’s bug bounty program. Following his report, Wordfence coordinated with the plugin developers to patch the flaw that impacted plugin release 7.11.0.

Eventually, the developers, Webnus, patched the flaw with the Modern Events Calendar 7.12.0. Besides, the researcher won a $3,094 bounty for the bug report.

While the patch has been released, Wordfence detected active exploitation attempts for this vulnerability. Given that the plugin boasts over 150,000 active installations, the flaw risks thousands of websites globally. Therefore, users must ensure updating their sites with the latest plugin release to avoid potential threats.

Let us know your thoughts in the comments.


[ad_2]
Source link
GuardZoo Android Malware Attacking Military Personnel via WhatsApp

0
[ad_1]

A Houthi-aligned group has been deploying Android surveillanceware called GuardZoo since October 2019 to target military personnel in the Middle East by leveraging social engineering tactics and using military-themed lures to trick victims into downloading the malware. 

Based on a preexisting RAT (Remote Access Trojan) called Dendroid, GuardZoo grants attackers remote control over the infected device, allowing for data exfiltration and potentially additional malware installations. 

The campaign remains active and has targeted users in Yemen, Saudi Arabia, Egypt, and Oman, as Google has confirmed that no GuardZoo-infected apps are currently available on Google Play. 

List of GuardZoo samples with dates and titles.

GuardZoo, a derivative of the leaked Dendroid RAT, utilizes a custom C2 backend built with ASP.NET instead of the original’s PHP web panel.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files

It communicates with its C2 server through its primary address, https://wwwgoogl.zapto[.]org and a backup at https://somrasdc.ddns[.]net. GuardZoo boasts over 60 commands, most exclusive to it and presumably added by the attacker, for various malicious tasks.  

List of C2 commands and functions.

An app can download and load external DEX files from a C2 server instead of requiring a full APK update, which is downloaded from “<C2 Address>/updateApp?dexfile=classes.dex” and placed in the app’s data directory’s “dex” folder. 

The app then restarts to load the new DEX file. While this secondary payload delivery method is deprecated, the code for DEX loading is still present, potentially allowing the app to revert to this method in the future. 

GuardZoo can download and dynamically load external DEX files.

GuardZoo, a Yemeni malware, utilizes dynamic DNS domains registered to YemenNet for C2 communication by employing self-signed certificates and using the ASP.NET backend on IIS 10. 

Upon infecting a device, GuardZoo establishes connection and retrieves initial commands: uploading specific geolocation files (KMZ, WPT, RTE, TRK) created after a set date, setting a 15-minute retry window on errors, disabling local logging, and uploading file metadata.

Communication is over HTTPS, but the request body is unencrypted. 

GuardZoo can upload the list of files to the device.

GuardZoo, a malware family, has been targeting devices in the Middle East since at least December 2022 by luring users with various themes, including military, religious, and ebooks, to trick users into installing it. 

The initial infection vectors are WhatsApp, WhatsApp Business, and browser downloads.

Unsecured C2 server logs reveal that victims are mostly located in Yemen, Saudi Arabia, and Egypt, with a smaller number in Oman, the United Arab Emirates, Turkey, and Qatar.

The logs also contain IP addresses and mobile carrier details of the victim devices. 

According to C2 server logs, victim IPs are scattered around Middle Eastern countries.

Analysis of the C2 server by Lookout revealed its purchase on March 18th, 2019, from a distributor in the United Arab Emirates, likely serving Yemen.

The codebase itself was primarily English, but the user interface and messages indicated Modern Standard Arabic usage. 

The timezone was set to “Asia/Baghdad” (GMT+3) and the project was named “Project 500” locally, while log entries suggested the targets were Pro-Hadi forces, Yemen’s internationally recognized government, further corroborated by an exfiltrated document referencing the Yemeni Ministry of Defense.

“Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!”- Free Demo


[ad_2]
Source link
A week in security (July 8 – July 14)

0
[ad_1]

July 12, 2024 – In a new malware campaign, threat actors are using Google ads to target Mac users looking to download Microsoft Teams.

July 12, 2024 – Customers of the stalkerware application mSpy had their customer support details exposed after a data breach

July 12, 2024 – AT&T has told customers about yet another data breach. This time call and text records of nearly all customers were stolen.

July 12, 2024 – Apple has sent a warning to people targeted by mercenary spyware in 98 countries.

July 8, 2024 – Shopify has denied it has suffered a breach, saying the stolen data comes from a third-party provider that will notify affected customers.


[ad_2]
Source link

Malicious NuGet Campaign Tricking Developers To Inject Malicious Code

0
[ad_1]

Hackers often target NuGet as it’s a popular package manager for .NET, which developers widely use to share and consume reusable code. 

Threat actors can distribute malicious code to many projects by compromising the NuGet packages.

In August 2023, ReversingLabs detected a malicious campaign against NuGet and noticed the change in techniques used by the threat actors.

Malicious NuGet Campaign

Earlier, they had been utilizing simple initialization scripts in more than 700 malignant packages and then switched to using *.targets files to exploit NuGet’s MSBuild integrations.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files

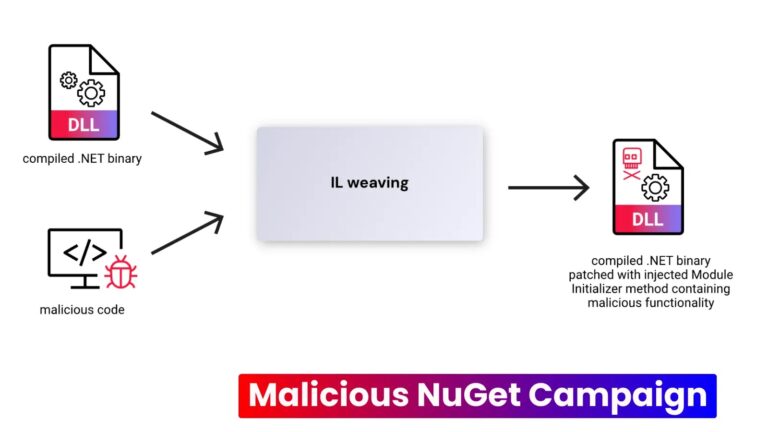
The most recent variant uses obfuscated downloaders incorporated into genuine PE binaries using IL weaving.

To appear trustworthy, there were attempts like impersonation, typosquatting, and artificially inflating download counts.

IL weaving (Source – ReversingLabs)

This attack is an example of how these attackers can adjust their tactics as well as grow their skills to compromise the .NET ecosystem further.

This threat actor has been persistently targeting NuGet for over six months with advanced skills that have evolved to use IL weaving techniques.

This method enhances the detection complexity, as it injects malicious module initializers into legitimate .NET binaries.

Lately, attacks include patching DLL files from popular packages such as Guna.UI2.WinForms and using typosquatting to bypass NuGet’s prefix reservation system. Obfuscated SeroXen RAT is downloaded using the injected code.

Package with a reserved prefix (Source – ReversingLabs)

After all, while analyzing compiled binaries might be more complicated than plaintext scripts, ReversingLabs Spectra Assure, among others, can identify suspicious functionalities in these altered packages, consequently illustrating a cat-and-mouse game between threat actors and security measures within the NET ecosystem.

Using homoglyphs to evade prefix reservations, researchers said the NuGet campaign produces packages that look real but aren’t.

Attackers used IL weaving to alter legal DLLs and injected obfuscated module initializers, making malware detection difficult.

About 60 packages and 290 versions were identified by ReversingLabs in this campaign, all of which had already been deleted on NuGet.

This attack’s emerging tactics in supply chain threats involve software such as binary patches and advanced typosquatting.

This is important as it shows that development organizations should be more cautious and use advanced detection techniques against these stealthy attacks aimed at open-source package managers.

“Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!”- Free Demo


[ad_2]
Source link

X investigated from the EU for possibly violating the Digital Services Act

0
[ad_1]

The European Union is regularly investigating big tech companies, and the latest company currently under scrutiny is X. The European Commission now claims X has violated the Digital Services Act (DSA), at least judging by the Commission’s preliminary findings.

It seems that the platform’s approach to paid verification is what is bothering the EU. Regulators say the practice “deceives users” and does not correspond to industry practice. The issue seems to be that since anyone can get a blue check-mark, it’s difficult to determine the authenticity of accounts. Also, there is, reportedly, evidence of bad actors using check-marks to trick people.

Paid check-marks seem to lead to an increase in scams and spam.

On top of that, the EU believes that X has a lack of advertising transparency. The EU claims that the tech giant doesn’t have a reliable, searchable ad repository. The EU says that X violates the DSA by failing to give researchers sufficient access to public data. According to the Commission, researchers are dissuaded from carrying out projects or forced to pay high fees to do their research.

-Thierry Breton, EU’s internal market commissioner


If the Commission finds that X is guilty, it can be fined up to six percent of its global annual revenue, which should be a pretty big sum. Also, the EU could direct X to ensure compliance with the DSA and impose further fines if the company fails to do so.

[ad_2]
Source link