Juniper SRX Vulnerability Allows Attackers Trigger DoS Condition

0
[ad_1]

A vulnerability in Junos OS on SRX Series devices allows attackers to trigger a DoS attack by sending crafted valid traffic, which is caused by improper handling of exceptional conditions within the Packet Forwarding Engine (PFE) and leads to PFE crashes and restarts upon receiving the specific traffic. 

An attacker can exploit this by continuously sending the malicious traffic, causing a sustained DoS condition and potentially impacting network resource availability. 

An unauthenticated attacker on the network could use a vulnerability in Junos OS versions starting with 21.4R1 to affect SRX Series devices by causing a Denial-of-Service (DoS) condition. 

Severity Assessment (CVSS) Score

This vulnerability, which achieves a high severity rating according to both CVSS v3 (7.5) and v4 (8.7) scoring systems, allows an attacker to crash a critical process (PFE) by sending specific valid traffic to the device, which will lead to a service outage until the device is rebooted.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo

A recently discovered vulnerability in Juniper’s Junos OS for SRX Series firewalls can cause a denial-of-service (DoS) condition, which exists in the Packet Forwarding Engine (PFE) and allows an unauthenticated attacker to crash the PFE through specifically crafted valid traffic. 

All Junos OS versions on SRX devices starting from 21.4R1 (including 21.4, 22.1, 22.2, 22.3, and 22.4) are susceptible if they haven’t been patched with the following updates: 21.4R3-S7.9, 22.1R3-S5.3, 22.2R3-S4.11, or 22.3R3 (for 22.3).

While Juniper has not identified any active exploitation, applying the security patches is crucial to mitigating potential DoS attacks. 

Software releases 21.4R3-S7.9, 22.1R3-S5.3, 22.2R3-S4.11, 22.3R3, 22.4R3, and 23.2R1, and all subsequent versions have been identified and resolved.

Be aware that versions 21.4R3-S7.9, 22.1R3-S5.3, and 22.2R3-S4.11 are updates of prior releases, so pay close attention to the complete version number, especially the last digits. 

The issue (1719594) identified on the Customer Support website cannot be evaluated by Juniper’s Security Incident Response Team (SIRT) because their policy excludes investigating releases that have surpassed either the End of Engineering (EOE) or the End of Life (EOL). 

The Security Incident Response Team (SIRT) inspects only software versions that are actively supported for security vulnerabilities. 

An issue was identified and documented on July 1st, 2024.

After investigation, it was determined that no temporary solutions or alternative methods (workarounds) are currently available to address this problem. This indicates that the issue is likely complex and may require a more permanent fix, such as a software patch or hardware update. 

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files


[ad_2]
Source link
Ulefone Note 18 Ultra benchmark test: Video

0
[ad_1]

The Ulefone Note 18 Ultra was announced as the first 5G smartphone in the company’s ‘Note’ lineup. That device was announced a while back and the Ulefone Note 18 Ultra benchmark/performance test video is now available.

The Ulefone Note 18 Ultra benchmark test is here… in a video format

This video was published on the company’s YouTube page, and it’s embedded below the article. It has a duration of about a minute and a half. In it, Ulefone visibly runs various benchmarks on the device, to show you the results.

You can easily check out the video below if you’d like to know more. Alternatively, we’ll talk a bit about the results now. First and foremost, do note that the Ulefone Note 18 Ultra comes with the MediaTek Dimensity 720 chip. That SoC has six cores.

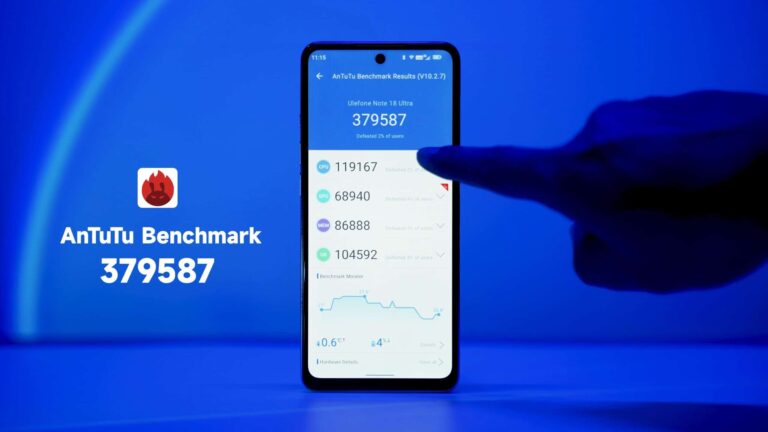
The first test is the AnTuTu test. It tests CPU, GPU, MEM (memory and storage), and UX (user experience). The phone managed to get a total score of 379,587 points. The CPU score was 119,167 points, a GPU score was 68,940 points, a MEM score was 86,888 points, and a UX score was 104,592 points.

Geekbench 6 is one of the tests used by Ulefone

Geekbench 6, on the other hand, tests single-core and multi-core performance. The Note 18 Ultra scored 640 points in the single-core test. When it comes to a multi-core test, it managed to score 104,592 points.

3DMark Wild Life test measures the overall gaming performance of the phone. The Ulefone Note 18 Ultra scored 1,340 points in that test.

PCMark is next. PCMark Work 3.0 was used, and it measures the performance and battery life of the device by mimicking regular tasks. The phone scored 9,107 points in the PCMark Work 3.0 test.

And finally, AndroBench. This one is focused on the phone’s storage. The Ulefone Note 18 Ultra managed to reach 854,44MB/s read and 194.81MB/s sequential write speeds.

You can check out all of this below. Also, do note that Ulefone is currently running a Euro 2024 contest. You can learn more about it via one of the links below, and win the Ulefone Armor 25T Pro even.

Ulefone Note 18 Ultra (more info)

Ulefone’s Euro 2024 contest

Ulefone Armor 25T Pro (more info)


[ad_2]
Source link

US government revoked eight Huawei export licenses in 2024

0
[ad_1]

In May, the US Department of Commerce said it had revoked “certain licenses” for exports to Huawei. It turns out the Joe Biden-led US government has canceled as many as eight licenses so far in 2024. This is the Biden administration’s latest effort to cripple the Chinese tech titan.

The US government revokes more licenses to contain Huawei’s growth

Huawei is fighting a battle like no other major tech company. The Chinese firm that once threatened to overthrow Samsung as the world’s largest smartphone company has been reduced to a shadow of itself by the US sanctions. This happened after the US government placed it on the Entity List in 2019. The Donald Trump administration labeled Huawei a national security threat over its potential ties with the Chinese government.

This effectively blocked the firm’s access to the latest smartphone technologies made or originated in the US. It couldn’t source advanced chips, Google services and apps, and other components and equipment to make powerful new 5G phones. The US government allowed some American companies to do business with Huawei by obtaining special licenses. However, those licenses still came with several restrictions.

The situation didn’t change when Joe Biden came into power in 2021. In the meantime, Huawei started building a domestic supply chain. Backed by the state fund and citizen’s sympathy, it is slowly rising from the ashes, at least in China. The special licenses enabled it to remain afloat in the industry during this difficult phase. The US government has realized this and has revoked some of those licenses to try and contain Huawei’s growth.

“We continuously assess how our controls can best protect our national security and foreign policy interests, taking into consideration a constantly changing threat environment and technological landscape. As part of this process, as we have done in the past, we sometimes revoke export licenses,” the Commerce Department said in May. A document seen by Reuters reveals the US government has revoked eight such licenses in 2024.

Qualcomm & Intel are among the affected companies

According to Reuters, the Commerce Department prepared this document in response to an inquiry by Republican Congressman Michael McCaul. The document doesn’t name the US companies whose licenses have been revoked. However, it was revealed in May that Qualcomm and Intel are among the affected companies. These chip firms are reportedly no longer doing any business with Huawei.

Licenses that are still valid include those for exports of “exercise equipment and office furniture and low-technology components for consumer mass-market items, such as touchpad and touchscreen sensors for tablets,” the new report states. Interestingly, the Commerce Department said it didn’t revoke these licenses because the said items are already “widely available in China from Chinese and foreign sources.”

The US government seems to be trying to block Huawei’s technological advancements in chipmaking. It recently launched powerful new phones with chips made by Chinese firm SMIC. This helped its smartphone sales grow 64% year on year in the first six weeks of 2024. It remains to be seen if the new moves derail the progress. Sooner or later, Huawei may eventually come out of the mess though.

[ad_2]
Source link

Affirm says Evolve Bank data breach also compromised some of its customers

0
[ad_1]

‘Buy now, pay later’ payment specialist Affirm has warned that holders of its payment cards had their personal information exposed after a ransomware attack and data breach at Evolve Bank & Trust.

In a form 8-K, submitted to the Securities and Exchange Commission (SEC), Affirm states:

“Because the Company [Affirm Holdings, Inc] shares the Personal Information of Affirm Card users with Evolve to facilitate the issuance and servicing of Affirm Cards, the Company believes that the Personal Information of Affirm Card users was compromised as part of Evolve’s cybersecurity incident.”

According to Evolve, the attack started after “an employee inadvertently clicked on a malicious internet link.” Evolve refused to pay the ransom, and so the attackers leaked the data they downloaded.

Affirm isn’t the only fintech company affected by the Evolve breach. Business bank Mercury also notified customers that the data stolen from Evolve Bank & Trust included some account numbers, deposit balances, business owner names, and emails associated with Mercury and other fintech accounts.

“Affected Mercury customers have been notified of the breach and the preventative steps we are taking to keep customer funds secure.”

Money transfer service and payment platform builder Wise also published a statement on its website, informing customers it had shared full names, addresses, contact details, Social Security numbers, and other sensitive information with Evolve as part of a partnership between 2020 and 2023.

So, it’s entirely possible that other financials may come forward with similar notifications. Reportedly, Evolve has active partnerships with multiple fintech companies, including Shopify, Bilt, Plaid, and Stripe.

Keep your eyes and ears open and be wary of phishing attempts related to these breaches.

Protecting yourself after a data breach

There are some actions you can take if you are, or suspect you may have been, the victim of a data breach.

  • Check the vendor’s advice. Every breach is different, so check with the vendor to find out what’s happened, and follow any specific advice they offer.
  • Change your password. You can make a stolen password useless to thieves by changing it. Choose a strong password that you don’t use for anything else. Better yet, let a password manager choose one for you.
  • Enable two-factor authentication (2FA). If you can, use a FIDO2-compliant hardware key, laptop or phone as your second factor. Some forms of two-factor authentication (2FA) can be phished just as easily as a password. 2FA that relies on a FIDO2 device can’t be phished.
  • Watch out for fake vendors. The thieves may contact you posing as the vendor. Check the vendor website to see if they are contacting victims, and verify the identity of anyone who contacts you using a different communication channel.
  • Take your time. Phishing attacks often impersonate people or brands you know, and use themes that require urgent attention, such as missed deliveries, account suspensions, and security alerts.
  • Consider not storing your card details. It’s definitely more convenient to get sites to remember your card details for you, but we highly recommend not storing that information on websites.
  • Set up identity monitoring. Identity monitoring alerts you if your personal information is found being traded illegally online, and helps you recover after.

Malwarebytes has a free tool for you to check how much of your personal data has been exposed online. Submit your email address (it’s best to give the one you most frequently use) to our free Digital Footprint scan and we’ll give you a report and recommendations.


[ad_2]
Source link

New Galaxy Z Flip 6 leak gives us fresh look at upcoming foldable

0
[ad_1]

Samsung is still a week away from its next Unpacked. But at this point, there is hardly anything that we don’t already know about the upcoming Galaxy devices. Leaks have already revealed their design, detailed specs, color options, alleged prices, and more. The leaks train isn’t stopping yet, with the Galaxy Z Flip 6 showing up in fresh images.

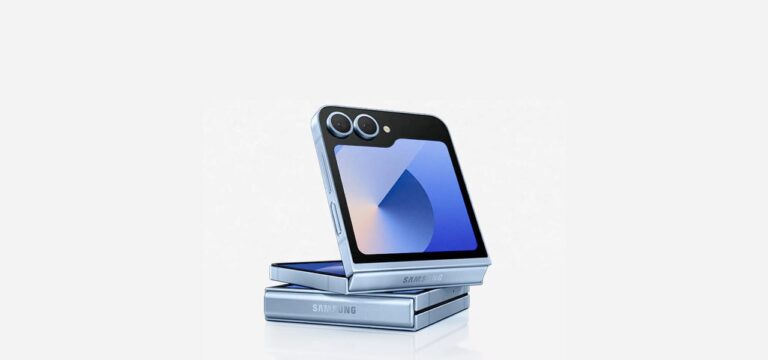
Leaked Galaxy Z Flip 6 images focus on the cover screen, aka Flex Window

Prolific leakster Evan Blass, aka Evleaks, recently posted several Galaxy Z Flip 6 images on X. The official-looking images focus on the new foldable’s cover screen, now also known as the Flex Window. Samsung redesigned the external display last year, making it bigger with a folder-shaped design allowing enough space for two rear-facing cameras and an LED flash unit. It’s keeping the same design this year.

A bigger cover screen lets you do a lot of things without unfolding the device. As shown in these leaked images, the Flex Window can display your health stats, weather, and more. It supports fullscreen widgets for the calendar, call log, clock, alarm, timer, contacts, dialer, and many other apps. You can also play games, make payments, reply to incoming messages, and do a lot more on the Filp 6’s cover display.

On top of this, Samsung’s Flex Cam mode allows you to use the cover display as the viewfinder for hands-free photos using the rear cameras. The Flex Window doesn’t support a full-fledged camera app but it’s still fairly feature-rich. You can capture amazing group photos with your friends without missing anyone. Just place the phone on a stable surface, turn on Flex Cam, and start capturing. The cover display also supports Good Lock customizations.

The upcoming Samsung foldable will be available in four colors

Samsung is preparing to release the Galaxy Z Flip 6 in Blue, Mint, Silver, and Yellow colors. We have already seen renders in all four colors. This leak shows the Blue variant up close. Like before, the Korean firm may offer the phone in a few other colorways exclusively through its online store. These additional colors may not be available globally. We will know for sure in a week. Samsung is expected to open pre-orders immediately after the launch event.

The Galaxy Z Flip 6 will be accompanied by the Galaxy Z Fold 6, Galaxy Watch 7, Galaxy Watch Ultra, Galaxy Buds 3, Galaxy Buds 3 Pro, and Galaxy Ring. Yes, the next Unpacked in Paris, France will be massively packed. You can pre-reserve these devices without commitment and get a $50 credit when you place your pre-order following their launch. Stick around for more leaks and rumors about Samsung’s upcoming Galaxy lineup.


[ad_2]
Source link

Global Xiaomi MIX Fold 4 is coming; here’s its design & specs

0
[ad_1]

The Xiaomi MIX Fold 4 is the company’s upcoming foldable, and its design and specs just surfaced. Before we get down to it, do note that the phone seems to be on the way to global markets.

The Xiaomi MIX Fold 4 is coming to global markets, its design & specs leak

It was about time for this to happen. The previous three iterations of the device were limited to China, which was a shame. Based on the information from Ice Universe, one of the best-known tipsters out there, the phone is coming to global markets. The Xiaomi MIX Flip will also be available outside of China, by the way.

Ice Universe also mentioned that the Xiaomi MIX Fold 4 will be extremely thin. It will be 9.Xmm thick, so similar to the upcoming HONOR Magic V3. That phone is also said to measure 9.9mm in thickness when folded. It remains to be seen which one will take the crown of the thinnest one, though.

With that in mind, Evan Blass aka evleaks, one of the best-known tipsters in the tech sphere, shared the phone’s image and some specs. You can check out the render he shared below.

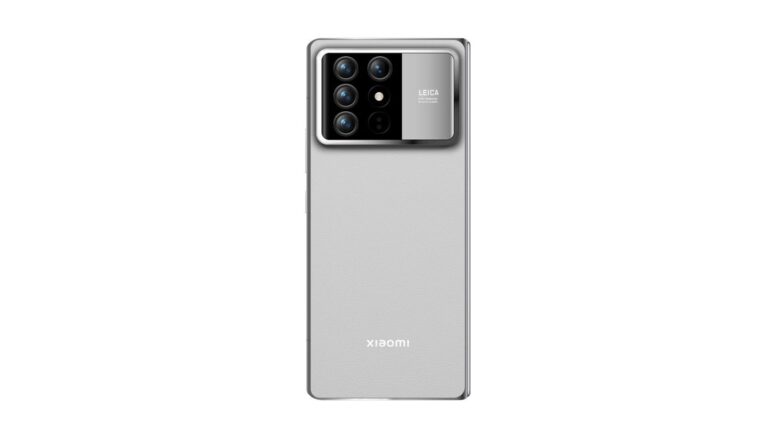
Xiaomi MIX Fold 4 design leak

The device will seemingly have four camera on the back, and Leica lenses

He did, however, mention that this render is a ‘work product’, so there’s a chance it’s not final. In any case, you will notice a huge camera island on the back. On the left side, four cameras seem to be located, along with an LED flash. On the left, the Leica logo and some sensor information.

The phone will be slightly curved in the corners, and it will seemingly be made out of metal and glass. A vegan leather variant is always a possibility when Xiaomi is concerned. That could help brush off some weight off the device too.

What about the specs? Well, Evan says that the Snapdragon 8 Gen 3 will fuel the phone, as expected. A 50-megapixel main camera will sit on the back, and Leica Summilux lens(es) will be in use.

A 5,000mAh battery is mentioned too, as is wireless charging support. The phone will be IPX8 rated for water resistance. Evan also mentioned that the phone will be less than 10mm thick when folded.


[ad_2]
Source link

HONOR Magic V3 design confirmed, camera improvements coming

0
[ad_1]

The HONOR Magic V3 has been all over the news lately. HONOR is looking to push the boundaries of foldable smartphone design once again. The HONOR Magic V3 design has just been confirmed, and some additional details were shared too.

HONOR just revealed the Magic V3 design, and it’s exciting

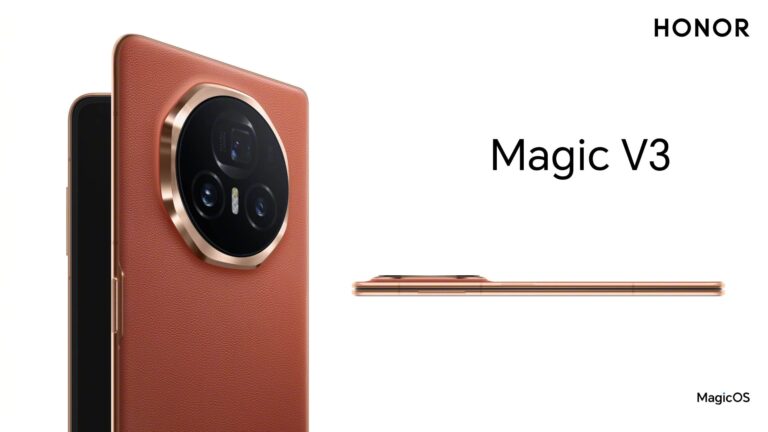
The company itself confirmed the phone’s design, and you can check it out in the gallery below. It’s obvious that HONOR is aiming to make the phone look a bit more similar to the Magic6 Pro. That camera oreo on the back is a dead giveaway.

HONOR Magic V3 official image 3

It has a similar camera placement to the Magic6 Pro. It’s not just for aesthetic purposes either. The HONOR Magic V3 is coming with a camera boost, more on that soon. You’ll notice that this orange variant has gold accents and a vegan leather backplate. It’s hard to deny it looks really nice. This model is referred to as ‘dark orange’, based on the tipster’s info. You can also check out the official promo video by clicking here.

The Magic Vs3 design was also confirmed by the company

It is worth noting that the Magic Vs3 design also got shared, you can check it out below this paragraph. A different camera oreo is included on the back for this one, with different camera placement.

HONOR Magic Vs3 offical image 1

The HONOR Magic V3 is the star of the show, though. That phone will be 9.Xmm thick based on the information shared thus far. It will also be quite light for a book-style foldable, as was its predecessor… allegedly even lighter.

HONOR is aiming to offer camera improvements this time around

What about its cameras? Well, Teme, a tipster, did share some information. The main camera will be a 50-megapixel ‘Eagle Eye’ camera. The phone will now include a periscope camera too, unlike its predecessor. A 3.5x optical zoom will be supported.

The tipster did clearly say that this time “HONOR also focuses on the camera side”. That is great to see. The Magic V2 had a good camera setup, but not flagship-worthy. The Magic V3 is looking to change that, it seems.

The HONOR Magic V3 and Vs3 will become official on July 12 in China. The global launch will follow later on, though hopefully sooner than it did for the Magic V2.

HONOR Magic V3 official image 4


[ad_2]
Source link

Critical WordPress Plugin Flaw Exposes 90,000+ WordPress Sites

0
[ad_1]

A critical vulnerability has been discovered in the popular WordPress plugin “Email Subscribers by Icegram Express – Email Marketing, Newsletters, Automation for WordPress & WooCommerce.”

The flaw, identified as CVE-2024-6172, has been assigned a CVSS score of 9.8, indicating its severe impact.

The vulnerability was publicly disclosed on July 1, 2024, and last updated on July 2, 2024, by the researcher known as shaman0x01 from the Shaman Red Team.

According to the Wordfence blog, the vulnerability affects all plugin versions up to and including 5.7.25.

It stems from insufficient escaping of the user-supplied db parameter and inadequate preparation on the existing SQL query.

This flaw allows unauthenticated attackers to execute time-based SQL Injection attacks, enabling them to append additional SQL queries into existing ones.

Consequently, attackers can extract sensitive information from the database, posing a significant risk to the security and privacy of the affected websites.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo

The “Email Subscribers by Icegram Express” plugin is widely used for email marketing, newsletters, and automation on WordPress and WooCommerce sites.

With over 90,000 active installations, the potential impact of this vulnerability is extensive.

Websites using this plugin are at risk of data breaches, which could expose sensitive user information, including email addresses, passwords, and other personal data.

Research and Discovery

The vulnerability was discovered by shaman0x01, a researcher from the Shaman Red Team, with a track record of identifying critical security flaws.

The researcher’s findings highlight the importance of proper input validation and query preparation in preventing SQL Injection attacks.

Notably, CVE-2024-37252 appears to duplicate this issue, underscoring the critical nature of the vulnerability.

Website administrators using the “Email Subscribers by Icegram Express” plugin are strongly advised to mitigate the risk immediately.

The following steps are recommended:

  1. Update the Plugin: Check for any available updates from the plugin developers and apply them as soon as possible.
  2. Disable the Plugin: If an update is unavailable, consider temporarily disabling the plugin to prevent potential exploitation.
  3. Monitor for Unusual Activity: Check your website for any signs of unusual activity, such as unexpected database queries or unauthorized access attempts.
  4. Backup Data: Regularly back up your website data to ensure you can restore it in case of a security breach.

The discovery of CVE-2024-6172 is a stark reminder of the importance of robust security practices in plugin development.

As WordPress remains a popular platform for websites worldwide, ensuring the security of its plugins is crucial to maintaining the integrity and privacy of online data.

Website administrators must stay vigilant and proactive in addressing vulnerabilities to protect their sites and users from potential threats.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files


[ad_2]
Source link
Hackers Claiming of Sandbox Escape RCE 0-DAY Google Chrome

0
[ad_1]

A group of hackers has claimed to have discovered a critical zero-day vulnerability in Google Chrome.

This exploit, which reportedly enables a sandbox escape and remote code execution (RCE), could potentially compromise millions of users worldwide.

The announcement was made via a post on the social media platform Twitter through the DarkWebInformer account.

The Vulnerability

As described by the hackers, the zero-day vulnerability allows for a sandbox escape, a technique that lets malicious code break out of the isolated environment designed to contain it.

"Is Your System Under Attack? Try Cynet XDR: Automated Detection & Response for Endpoints, Networks, & Users!"- Free Demo

This escape is coupled with remote code execution, meaning an attacker could run arbitrary code on a victim’s machine.

Such a combination is hazardous, as it can lead to full system compromise without any user interaction beyond visiting a malicious website or opening a compromised file.

Google Chrome, the world’s most popular web browser, relies heavily on its sandboxing technology to protect users from malicious code.

The sandbox isolates web content from the rest of the operating system, making it difficult for attackers to cause significant harm.

However, if the hackers’ claims are accurate, this new exploit could render these protections ineffective, posing a severe threat to user security.

Hacker Claims and Community Response

The hackers’ announcement on X has garnered significant attention from cybersecurity experts and enthusiasts.

The post included a cryptic message hinting at the technical prowess required to discover and exploit this vulnerability, suggesting that less sophisticated actors may not easily replicate it.

Cybersecurity professionals have expressed concern over the potential implications of this exploit.

“A sandbox escape combined with RCE in Chrome is a nightmare scenario,” said Jane Doe, a cybersecurity analyst at SecureTech.

“It could allow attackers to bypass all the security measures that users rely on to keep their data safe.”

In response to the claims, Google issued a statement acknowledging the report and assuring users that it is investigating the matter.

“We take all security threats seriously and are working to verify the claims made by DarkWebInformer. Our priority is to ensure the safety and security of our users,” a Google spokesperson said.

Google is known for its rapid response to security threats, often releasing patches within days of discovering vulnerabilities.

Users are advised to keep their browsers updated and follow best online security practices, such as avoiding suspicious links and downloading software only from trusted sources.

As the investigation continues, the cybersecurity community remains on high alert.

The discovery of such a critical vulnerability underscores the ongoing cat-and-mouse game between hackers and security professionals, highlighting the importance of vigilance and proactive security measures in the digital age.

Are you from SOC/DFIR Teams? - Sign up for a free ANY.RUN account! to Analyse Advanced Malware Files


[ad_2]
Source link
Special Google Messages icon for iOS-Android RCS chats has been removed

0
[ad_1]
With iOS 18 developer beta 2 installed, iPhone users subscribed to AT&T, T-Mobile, or Verizon can start messaging with their Android packing pals, relatives, and co-workers using RCS. This brings features such as read receipts, typing indicators, high-quality images, and videos to chats between iOS and Android users. Some of these features haven’t been working yet, typical for a beta release.
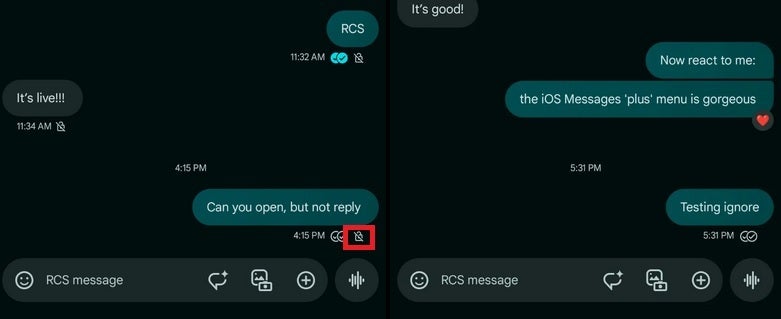
Apple iPhone-Android RCS messages do not support end-to-end encryption at the moment which had been indicated on Google Messages by a lock icon with a slash through the icon. Google Messages has its own end-to-encryption for one-to-one and group chats that Apple is not supporting. The icon itself was seen underneath each message sent and received over Google Messages when an Android user was chatting to an iPhone user with RCS support. If you’re wondering why I’m writing this in the past tense, it’s because, as of today, the ‘no end-to-end encryption’ icon has disappeared from Google Messages. 
One report says that the removal of the ‘no end-to-end encryption’ icon is due to a server-side update related to beta releases of Google Messages. There really is no reason for Google to continue to show the ‘no end-to-end encryption’ icon since there is nothing an iPhone user can do to remove that slash that covers the lock icon. 
As of now, the version of RCS supported by iOS does not include end-to-end encryption. It does encrypt messages in transit but your carrier will be able to read all of your messages. What will happen to end-to-end encryption when the stable version of iOS 18 is released is unknown but we can tell you that the text bubbles will remain green when an iPhone user is chatting with an Android user over RCS. Whether that means green bubble bullying by iPhone users will continue only time will tell.

Out of all of the improvements that iPhone and Android users will experience with the features available to them with the iOS support of RCS, perhaps the best is the way images and videos sent and received will appear. Previously, when iPhone and Android users had to message each other using SMS and MMS, shared pictures were often blurry and out of focus. Videos were hard to view, too. But that can come to an end right now if you feel like gambling on installing the iOS 18 developer beta.

With the drop in battery life and the typical iOS beta bugs, you might be better served by waiting for the stable version to be released later this year. By then, we might see iOS add Google Messages’ end-to-end encryption with its RCS support.


[ad_2]
Source link